- TESIGN / RADAR
- 2026.09.17
- OpenHunterAI
OpenHunterAI
Local AI red-team workspace
WHO USES ITA small team that wants to regularly check its own service's security · A developer who wants a coding agent to run approval-gated security checks · Anyone who wants hands-on practice with recon tooling, strictly on authorized targets
Self-host
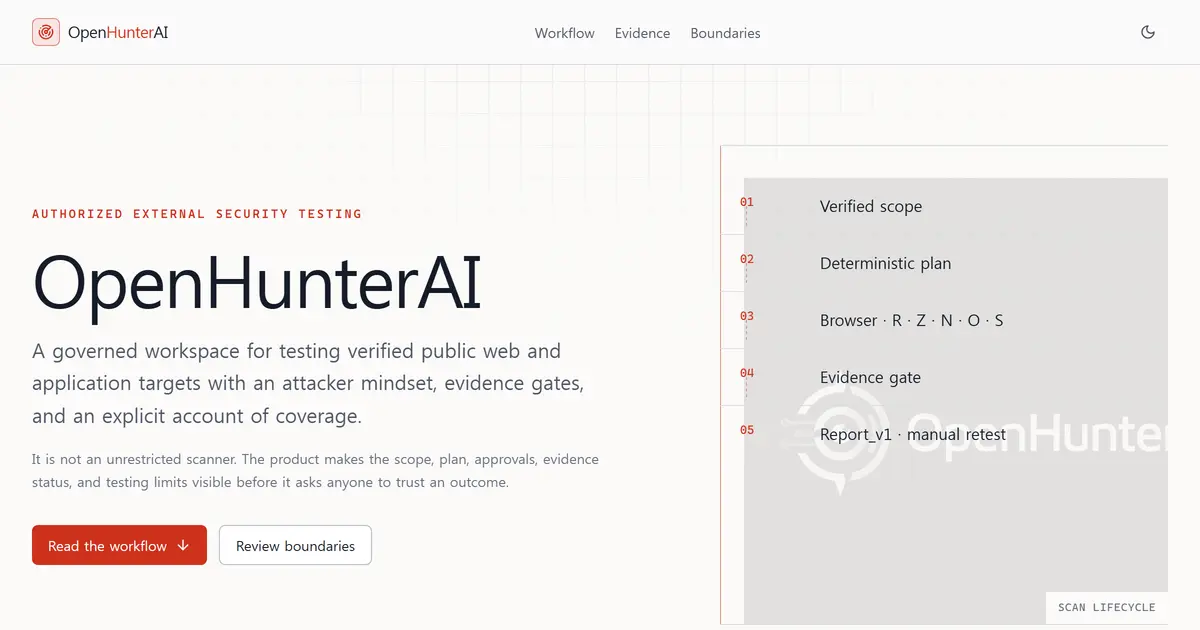
An alpha-stage local workspace that runs attacker-style security assessments — strictly against public targets you own or are authorized to test.
165 stars · checked on GitHub GitHub check 46 h late · incl. +2 observed via GH Archive since then · 7-day +15 observed via GH Archive (as of )
TESIGN TAKE
A security tool that calls itself alpha and states upfront that an empty report proves nothing is rare, and that honesty is itself reassuring.
AT A GLANCE
- USAGE
- Unconfirmed — check before use.
- LANGUAGE
- TypeScript
- PLATFORM
- web · cli
- ACTIVITY
- last commit 2 days ago () · latest release [unconfirmed]
- COMMUNITY
- contributors [unconfirmed] · open issues [unconfirmed] · made by: [unconfirmed] Reference time unavailable
- SOURCES
- GitHub
- FIRST SEEN
- CATEGORY
- SECURITY · AI
A summary, not legal advice.
WHY IT MATTERS
OpenHunterAI brings scope, scan activity, findings and remediation guidance into one local workspace with no signup. It only proceeds after verifying domain ownership and getting human approval on the scan plan, gathering signals through browser inspection, recon, ZAP and a Nuclei adapter for the AI to test bounded hypotheses against. As its own README states, it's alpha software — "a healthy workspace or an empty report does not prove a target is secure" — and it avoids destructive actions, gating sensitive validation behind separate approval.
BUILD FROM THIS
- Run an attacker-style checklist against your own web app or API before a release
- Wire it into a coding agent (Codex, Claude Code, Gemini CLI) as a skill so a scan only starts after explicit approval
- Use its report/retest flow as a template for a human-verified security review process
WHO IT'S FOR
- A small team that wants to regularly check its own service's security
- A developer who wants a coding agent to run approval-gated security checks
- Anyone who wants hands-on practice with recon tooling, strictly on authorized targets
START IN 5 MINUTES
# Requires Git, Node.js 22+, Docker with Compose v2
$ git clone https://github.com/LumosLab-Innovation/OpenHunterAI.git
$ cd OpenHunterAI
$ node ops/local.mjs start
# → open http://localhost:3001, set model keys in .env.local, create a project, verify its domain, approve scope, then start a scan
# (resolve the documented Nuclei template-policy blocker before scanning)CAVEATS
- PolyForm Noncommercial 1.0.0 — source-available; commercial use needs a separate licence
- Alpha stage; the README states plainly that an empty report does not prove a target is secure
- "Local" means the workspace runs on your machine, not permission to scan localhost or private networks; the Nuclei adapter doesn't yet ship a reviewed template bundle
RECEIPT
- FIRST SEEN
- AT SOURCE
- KEPT
- CREATED → FIRST SEEN
- 112d
- WHEN FIRST SEEN
- 163 ★
- SOURCES
- GitHub
The same facts in machine-readable form — View as Markdown · JSON
SIMILAR TOOLS
Up to five from SECURITY by ★ total: edited entries first, then repository cards; this entry is highlighted. Drawn from the same stored snapshot as the rankings — a comparison, not a recommendation.
| IMAGE | NAME | ★ TOTAL | ▲ 7d | LICENSE | PLATFORM | LAST PUSH |
|---|---|---|---|---|---|---|
 | open-code-reviewAI code review for developers | ★ 28.6k | ▲ +1,064 | Apache-2.0permissive | windows · macos · linux · cli | |
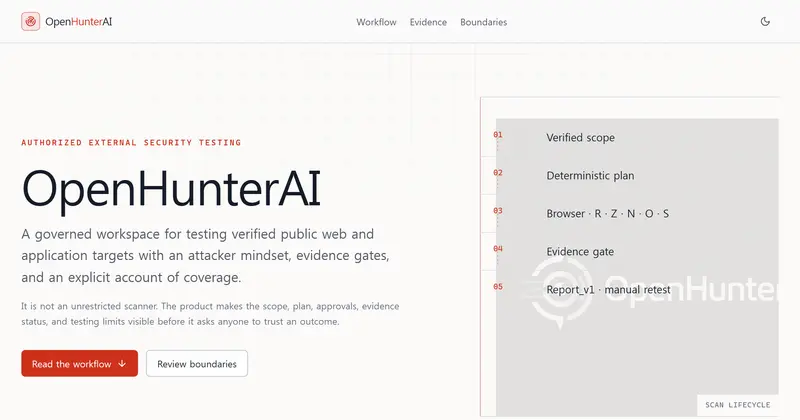 | OpenHunterAILocal AI red-team workspaceTHIS ENTRY | ★ 165 | ▲ +15 | Licence unconfirmedunconfirmed | web · cli | |
| ente/enteCARD | ★ 28.9k | ▲ +13 | AGPL-3.0copyleft | — | ||
| deskflow/deskflowCARD | ★ 28.8k | ▲ +5 | GPL-2.0copyleft | — | ||
| laramies/theharvesterCARD | ★ 17.4k | ▲ +10 | Licence unconfirmedunconfirmed | — |
ALSO WORTH SEEING
TIMELINE
- Repository created
- FIRST SEEN BY TESIGN
- Published on TESIGN
SAME DAY
- 01
BG0
No-account background removerRemoves a photo's background entirely inside your browser — no upload, no server, no account.
Use in the browser★ 79▲ +28 / 7d - 02
ZapFast
Lightweight native WhatsApp clientA from-scratch Rust WhatsApp client with no browser engine — about 150MB idle RAM on Linux, versus 1.13GB for WhatsApp Web.
Install to use★ 107▲ +39 / 7d - 03
Wealthfolio
Local-first personal finance trackerAn open-source portfolio tracker that keeps investments, net worth and spending entirely on your device — no cloud account.
Install to use★ 9k▲ +15 / 7d - 04
page-mascot
Cursor-following page mascotA tiny React component that puts a character on your page which turns its head to follow the cursor and reacts when clicked.
For developers★ 307▲ +39 / 7d - 05
Podroid
Linux container VM for your phoneBoots a real, separately-kernelled Alpine Linux VM on an unrooted Android phone, running Podman, Docker and LXC exactly as they behave on a server.
Install to use★ 2.6k▲ +14 / 7d - 06
Capsule
Single-file app playerA desktop player that packs an HTML app and its data into one SQLite file — no account, no server, just a file to share.
Install to use▲ 333 HN - 07
SparkyFitness
Self-hosted family health trackingA self-hosted health tracker for nutrition, exercise, sleep, fasting, mood and body metrics — all on a server you run yourself.
Self-host★ 6.1k▲ +13 / 7d - 08
Inkstone
Self-hosted notebook on CloudflareA self-hosted Markdown notebook you deploy on your own Cloudflare Workers account, with realtime sync, search and backlinks built in.
Self-host★ 819▲ +10 / 7d - 09
MartinLoop
Execution-control CLI for coding agentsWraps a coding agent with a spend cap and a verifier, so "I'm done" comes with an evidence-backed receipt instead of just a claim.
★ 130▲ +21 / 7d